What Triggered the Security Alarm?
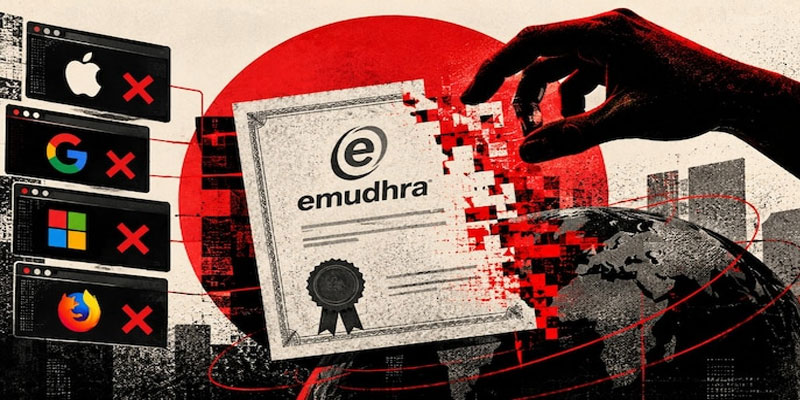
What’s the eMudhra security scare that has rattled the internet? The incident has exposed a serious vulnerability in the digital trust infrastructure underpinning secure internet communications. Eight intermediate certificate-authority certificates issued by Bengaluru-based eMudhra reportedly contained cryptographically weak private keys, potentially allowing attackers to forge trusted digital certificates and impersonate legitimate websites. Major browser developers have moved to block the affected certificates, while India’s Ministry of Electronics and Information Technology (MeitY) has ordered an investigation.
How the Vulnerability Compromised Digital Trust
eMudhra operates as a licensed Certifying Authority, issuing digital certificates that help browsers, operating systems and applications verify identities and establish secure connections. On October 17, 2026, an independent researcher reported that private keys associated with eight intermediate certificates were dangerously weak because of insufficient randomness during key generation.
Instead of providing the intended cryptographic protection, some keys were reportedly so small that researchers could reconstruct them in less than a second.
Possession of these keys could potentially allow malicious actors to create fraudulent certificates for domains they did not own. This could facilitate convincing fake websites, interception of communications or malicious software masquerading as legitimately signed content.
Emergency Measures and Investigation
eMudhra revoked all eight affected intermediate certificates on October 18. The company stated that no end-user website certificates had been issued through them, its infrastructure had not been breached and no data had been compromised. It also initiated certificate replacement for potentially affected customers.
Major technology companies responded with protective measures:
· Google: Announced plans to remove eMudhra’s emSign ECC Root CA-G3 from Chrome’s trusted certificate list on October 27.
· Mozilla: Removed the affected root authority from its trusted root list.
· Apple and Microsoft: Took steps to block the affected certificates through their security systems.
· MeitY: Established a special team to investigate the incident and assess its impact.
The government indicated that the impact on Indian websites and applications appeared limited and short-lived. Nevertheless, the episode has raised concerns about the security oversight of certificate authorities operating within the global digital ecosystem.
What Everyone Needs to Know
Ordinary internet users need not panic, but basic precautions remain important.
· Update browsers and operating systems: Security updates help enforce revised certificate-trust decisions.
· Watch for website errors: Some legitimate services may experience temporary disruptions while replacing affected certificates.
· Businesses must audit certificates: Organisations using eMudhra or emSign services should verify their certificate chains and replace affected credentials.
· Treat HTTPS cautiously: The padlock symbol indicates an encrypted connection, but does not independently guarantee that a website or its certificate authority is trustworthy.
Restoring Trust Requires Stronger Digital Safeguards
The eMudhra incident demonstrates that internet security depends on more than encryption. It also relies on the integrity of the institutions and cryptographic keys that establish digital identities. Although the reported exposure appears limited, the episode reinforces the need for rigorous key-generation procedures, independent security audits and rapid incident response. Ultimately, maintaining public confidence in digital services requires certificate authorities to meet the highest standards of security, accountability and transparency.
(With agency inputs)