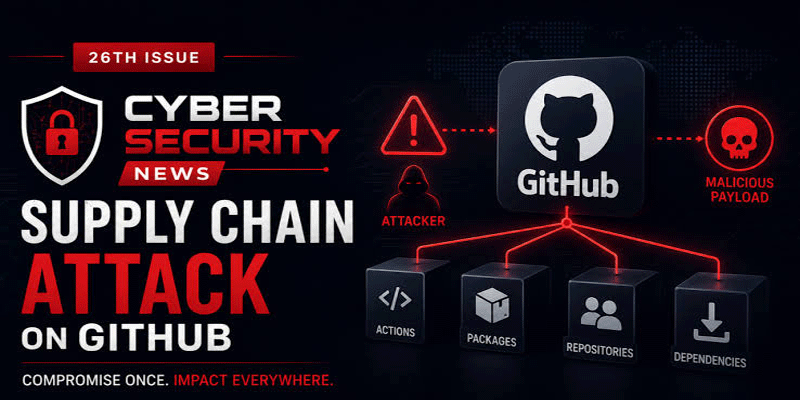
A security investigation has demonstrated how quickly a seemingly peripheral application can become a gateway into highly sensitive enterprise systems. Three researchers reportedly moved from a vulnerability in OpenAI’s public community forum to its private GitHub environment in less than 72 hours.
The initial entry point was a vulnerability involving libheif, an image-decoding library used within OpenAI’s Discourse-based community forum. Exploiting the flaw allowed the researchers to move beyond what might ordinarily be considered a relatively low-risk public-facing application.
The research also highlights the changing role of AI in offensive security. Anthropic’s Claude reportedly accelerated exploit development, helping researchers analyze vulnerabilities and develop techniques faster. However, the AI did not autonomously conduct the attack; human researchers directed the individual steps.
More concerning was what happened after the initial compromise. An SSO-related weakness reportedly created a pathway from the forum environment into employee services, including ChatGPT and Codex accounts, eventually providing access to OpenAI’s private GitHub environment.
The incident illustrates why vulnerability severity cannot be evaluated solely by looking at the compromised application. A community forum may appear less critical than production infrastructure, but interconnected identities, authentication systems and developer environments can dramatically increase its effective attack surface.
For CISOs, the lesson is to think in terms of attack paths rather than isolated assets. Security teams should continuously map trust relationships across SSO, SaaS applications, developer platforms and cloud environments, while enforcing least privilege and segmentation.
The critical question is therefore changing from “How important is this application?” to “If this application is compromised, what else can the attacker reach?” That shift is fundamental to modern Zero Trust and exposure management.